POST-DELIVERY EMAIL THREAT RESPONSE
Detection Is Not the Outcome, Control Is
ORQET analyzes reported emails, delivers human-derived verdicts, automates remediation, and turns confirmed attacks into tactical and technical threat intelligence.
Built for the reality that phishing still reaches the inbox, ORQET provides a structured approach to Post-Delivery Email Threat Response that combines AI-assisted technology with expert human analysis. Originally launched as PhishQueue, the platform has been in production since 2020.
Measured across ORQET customer environments.
Detection Identifies The Threat, ORQET Takes Action
Security tools can identify suspicious activity, but detection alone does not guarantee the right response, the right remediation, or the right outcome.


Threats still reach users’ inboxes. Security teams are forced to make fast decisions with incomplete context, while response actions often require coordination across users, analysts, and systems. Valuable threat intelligence is frequently lost once an incident is closed. As threats progress beyond delivery, complexity and business impact increase significantly. ORQET analyzes all reported emails, delivers clear verdicts to users, automates remediation of confirmed threats, and turns attacks into tactical and technical threat intelligence security teams can use.
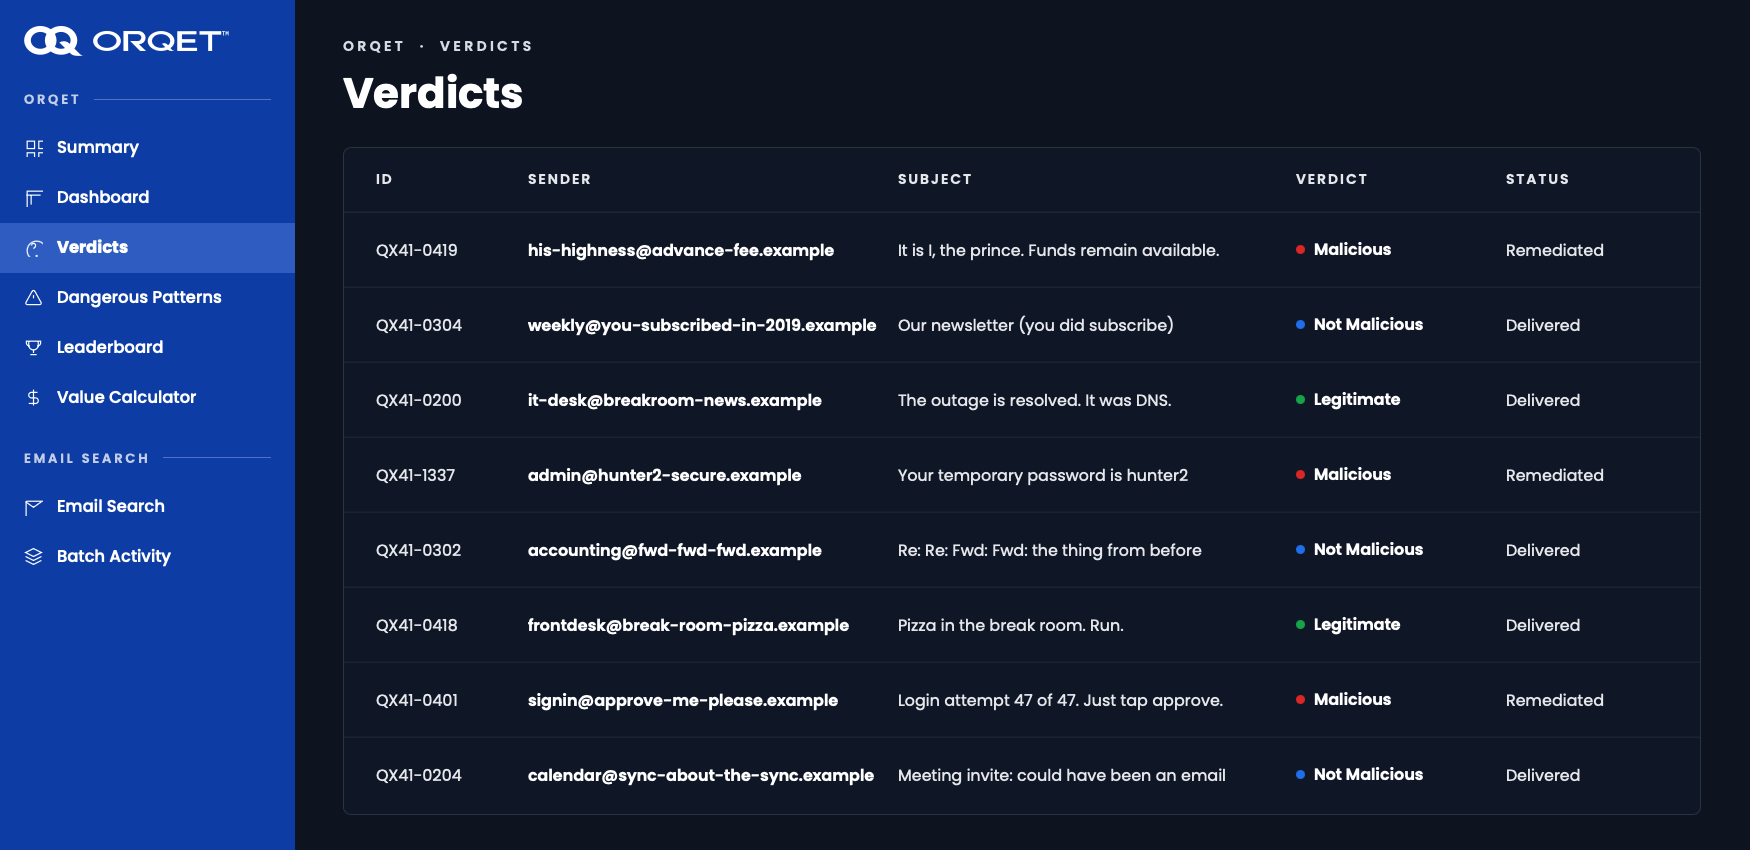
Interface shown is illustrative, for informational purposes only, and does not depict actual customer data or specific outcomes. Features and displays may vary by deployment model.
IBM and Ponemon Institute, Cost of a Data Breach Report 2025. Phishing is an initial attack vector.
Based on ORQET customer data regarding user-reported emails confirmed as threats.
62% of data breaches involve the human element.Verizon, 2026 Data Breach Investigations Report, 19th Edition.
How ORQET Works
Support Across the Post-Delivery Lifecycle
Post-delivery response is not a single stage. It moves through the four stages below.
Report
Users submit suspicious emails to ORQET for analysis.

Verdict
ORQET returns a clear verdict with human analyst involvement. Safe emails stop here; confirmed malicious emails move to remediation.
Remediation
When an email is confirmed as malicious, Search and Purge removes matching messages from affected mailboxes.
Threat Intelligence
Indicators and investigative context from confirmed threats are captured and enriched to provide tactical and technical threat intelligence.
Why ORQET Is Different
Most email security platforms focus primarily on prevention and detection. Post-Delivery Email Threat Response addresses what happens after delivery: determining whether a reported email is malicious, removing confirmed threats from affected mailboxes, and capturing the indicators and investigative context that can be used as tactical and technical threat intelligence.
ORQET focuses on what happens when suspicious emails reach the inbox, providing clear verdicts with human analyst involvement, customized instructions based on your organization’s requirements, and automated remediation when a threat is confirmed.
ORQET was built to bring these capabilities together, from the initial user report and verdict through automated Search and Purge and threat intelligence, providing organizations with a structured approach to responding to malicious emails that bypass existing email security.
Platform Outcomes
Designed to Deliver Greater Post-Delivery Control
ORQET confirms whether reported suspicious emails are malicious, automatically remediates confirmed threats, and turns attacks into threat intelligence that strengthens future response.
Reduced Dwell Time
Reported suspicious emails are analyzed and confirmed threats are automatically remediated, reducing the time malicious emails remain in affected mailboxes.
Reduces Analyst
Burden
Reduces repetitive investigation and remediation tasks so security teams can focus on higher-priority threats that matter most.
Consistent Responses
Clear verdicts with human analyst involvement bring judgment and context to reported suspicious emails, providing a consistent response through verdict.
Expanded Threat Visibility
See which emails were reported, which were confirmed malicious, and the IOCs and investigative context identified from those threats.
Detection Alone Versus Complete Response
The same reported email, two very different operating postures
DETECTION ALONE
- Detection only
- Manual triage
- Reactive response
- Limited visibility
- Fragmented workflows
Capability availability varies by deployment model.
Where ORQET Fits
Designed to Complement and Extend Your Existing Security Stack
ORQET works alongside secure email gateways, SIEM platforms, SOAR systems, EDR/XDR solutions, and your existing security stack. Through an API and STIX/TAXII feed, confirmed threat indicators and tactical and technical threat intelligence can be shared with existing security investments.